DFARS 252.204-7997 was called DFARS 252.204-7020 until it was changed under the Revolutionary FAR Overhaul (RFO) in 2026. It requires defense contractors handling Controlled Unclassified Information (CUI) to undergo National Institute of Standards and Technology (NIST) SP 800‑171 Department of War (DoW) Assessments and provide the government access to facilities, systems, and personnel for Medium and High Assessments.
Speak with our team
What is the difference between DFARS 7020 and DFARS 7997?
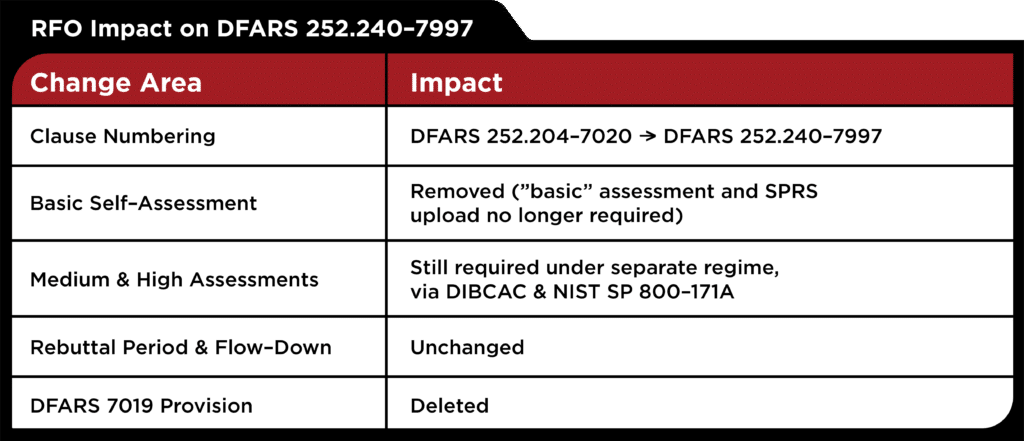
In its mission to simplify FAR requirements, the RFO removed the DFARS 7020 basic self-assessment and the entirety of DFARS 7019 in 2026. They also renumbered DFARS 252.204-7020 to DFARS 252.240-7997.
Under the previous structure, DFARS 7020 required strict flow-down. Contractors had to ensure that subcontractors possessed a current Supplier Performance Risk System (SPRS) score under DFARS 7019 before awarding any subcontract. That was before the RFO eliminated DFARS 7019 and renumbered and revised DFARS 7020. Oversight and flow-down requirements remain, but self‑assessment obligations now fall under DFARS 7021 (Cybersecurity Maturity Model Certification [CMMC]).
DFARS 252.204‑7020 Background
Before the RFO, DFARS 7020 required a Basic self‑assessment against NIST SP 800‑171, and DFARS 7020-supported enforcement through Medium and High Assessments, access requirements, and subcontractor flow-down.
The DoW implemented these clauses because DFARS 7012 lacked a validation mechanism; the DoW must verify compliance to fortify sensitive defense information.
DFARS 252.240-7997 Assessment Requirements
The clause applies to contractor information systems handling CUI that must comply with NIST SP 800‑171 under DFARS 252.204‑7012. Solicitations for Commercial Off-The-Shelf (COTS) items are exempt.
DFARS 7997 requires government access to contractor facilities, systems, and personnel any time the DoW is renewing or conducting a “NIST SP 800-171 DoD Assessment.” This is separate from a CMMC Assessment.
While 7997 doesn’t include a basic self-assessment, it does include Medium and High Assessments conducted by Defense Industrial Base Cybersecurity Assessment Center (DIBAC) at its own discretion. Not every contractor will be subject to a Medium or High Assessment.
Medium Assessment
DIBCAC may select an organization for Medium Assessment randomly, due to concerns from a contracting officer, program office request, or whistleblower tips.
In a Medium Assessment, DIBCAC reviews contractor documentation and seeks clarifications from the contractor where needed. The assessment results in a “Medium confidence” score.
If the Medium Assessment finds discrepancies, DIBCAC may escalate to a High Assessment or pursue False Claims Act charges.
High Assessment
High Assessments may also come from a random sampling, but specific risk factors or an escalation from a Medium Assessment are more common triggers. A High Assessment usually involves higher-risk CUI, or a program with elevated national security concerns.
The assessment includes document review and verification, examination, and demonstration of the system’s security implementation. There is also an in‑person validation of NIST SP 800‑171 controls. The assessment results in a “High confidence” score.
A poor assessment score can cause immediate changes to contract eligibility.
14‑Day Remediation Period
Contractors have a 14-day period to rebut their results by providing additional evidence or information demonstrating that their practices and policies meet NIST 800-171 standards. SPRS will only reflect the final assessment results after this period. All results are confidential, and High Assessment documentation will be classified as CUI.
DFARS 7997 vs. CMMC
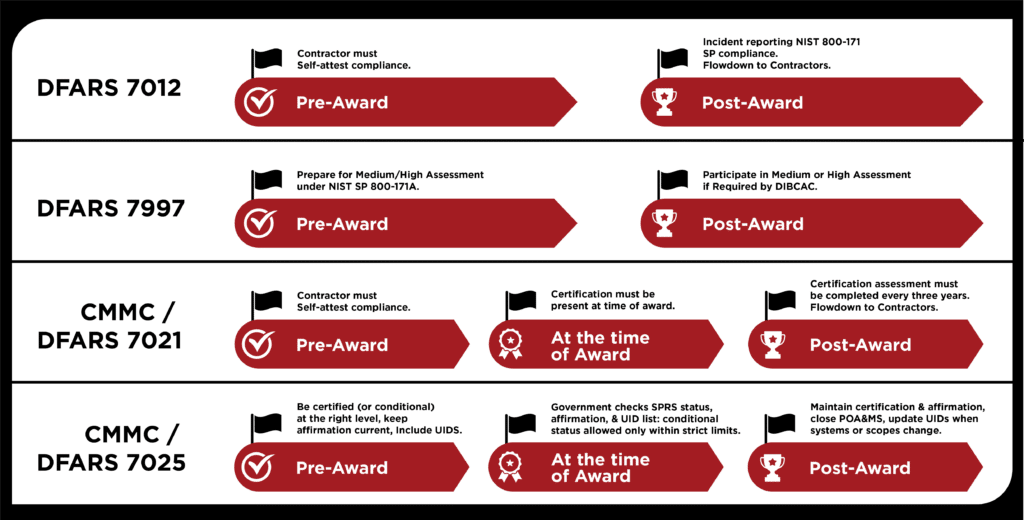
DFARS 7997 operates alongside DFARS 252.204-7021, which includes CMMC requirements for certain contracts. It will still focus on the NIST SP 800-171 DoD Assessments, but the updated rule will strengthen flow-down requirements. As the CMMC rule is phased in, the DoW will have discretion in applying DFARS 7997 assessments to solicitations based on risk and contract type.
Next Steps
Future acquisitions and solicitations determine if a Medium or High Assessment is in your near future. Your organization should configure its information systems to the 110 NIST 800-171 controls regardless because of CMMC 2.0 assessment requirements and the preexisting DFARS 7012 requirements.
Large primes, such as Lockheed Martin, have begun distributing questionnaires and data calls to subs. Prepare your proposal or business development teams to respond appropriately when asked for status.
To ensure that you meet DFARS 7020 and other requirements for DoW suppliers with enough time to remain competitive and future-proof your business, reach out to Summit 7’s compliance experts. d to request access through the Procurement Integrated Enterprise Environment (PIEE). Keep in mind you will need a certificate from a DoW-approved External Certificate Authority (ECA) vendor to register /authenticate to PIEE / SPRS.
To ensure you meet DFARS 7020 and other requirements for Department of War suppliers in enough time to remain competitive and future-proof your business, reach out to Summit 7’s compliance experts.
Contact
Speak With Our Team
Our team of compliance and cybersecurity experts are on standby and ready to help. We’ll walk you through what you need and what to expect.